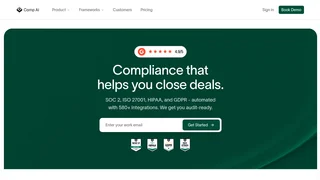
Comp AI is an open-source, agentic compliance and governance, risk, and compliance platform engineered to automate security certifications and continuous posture monitoring. Built to help fast-growing startups and software enterprises achieve and maintain frameworks such as SOC 2 Type I and Type II, ISO 27001, HIPAA, and GDPR, Comp AI replaces manual screenshot collection and rigid compliance templates with intelligent autonomous agents and verifiable evidence pipelines.
Autonomous Evidence Collection Across 580+ Integrations
Modern compliance audits fail primarily due to stale evidence and slow manual document gathering. Comp AI resolves this through autonomous AI workers that connect directly to more than 580 cloud and SaaS services. The platform interfaces with major infrastructure providers including Amazon Web Services, Google Cloud Platform, Microsoft Azure, GitHub, GitLab, Okta, Google Workspace, Datadog, Slack, and leading human resource information systems. Autonomous agents regularly query system APIs, capture timestamped configuration records, and verify that security controls remain continuously active.
Context-Aware Security Policy Generation
Rather than providing boilerplate policy templates that fail to reflect actual engineering practices, Comp AI analyzes an organization's specific technical architecture, team size, cloud topography, and operational workflows. It synthesizes tailored, auditor-ready security policies covering data retention, access control, incident response, vendor risk management, and employee onboarding. Founders and compliance leaders can review, edit, and approve each generated policy before formal publication.
Audit Readiness Timelines and Preparation Milestones
By automating the discovery and cataloging of infrastructure controls, Comp AI substantially compresses audit preparation timelines. While conventional compliance consulting engagements often demand three to six months of manual preparation, organizations leveraging Comp AI typically achieve readiness for SOC 2 Type I audits within approximately ten business days, allowing founders to unblock enterprise sales cycles rapidly.
Continuous Compliance Monitoring and Real-Time Remediation
Achieving compliance is not a static one-time achievement. Comp AI continuously monitors connected production infrastructure for configuration drift, exposed cloud storage buckets, unencrypted databases, missing multi-factor authentication enforcement, and overdue access reviews. When a control falls out of alignment, the platform generates immediate remediation instructions and creates tracking tickets for engineering teams to resolve vulnerabilities before audit windows open.
Vendor Risk Management and Automated Security Questionnaires
Assessing third-party vendor risk is a major bottleneck in modern security reviews. Comp AI includes automated vendor assessment tools that catalog all external SaaS providers, evaluate vendor security posture, and generate responses to complex incoming security questionnaires from prospective enterprise customers. The AI assistant parses questionnaires, matches questions against existing compliance evidence, and auto-fills verified responses in minutes.
Employee Onboarding and Security Awareness Tracking
Maintaining compliance requires active staff participation. Comp AI tracks employee security training completion, enforces device management controls like disk encryption and screen lock timeouts, and logs background check verification. Automated reminders notify team members when periodic security modules or policy re-acknowledgments are due.
Integrated Penetration Testing and Auditor Collaboration
Comp AI is designed to be completely auditor-agnostic. The system organizes evidence into structured, searchable control rooms where independent accredited CPA firms and certification bodies can verify tests quickly. Additionally, Comp AI coordinates included penetration testing workflows, allowing companies to fulfill technical assessment requirements alongside policy documentation in a single unified dashboard.
Open-Source Transparency and Self-Hosting Capabilities
Unlike proprietary compliance platforms that operate as black boxes, Comp AI maintains an open-source codebase on GitHub. Security teams can inspect evidence collection scripts, verify control logic, and maintain full data sovereignty without proprietary vendor lock-in.
Pricing, Self-Service Tools, and Enterprise Tiers
Comp AI offers flexible onboarding options suitable for early-stage teams through large enterprise deployments.
| Plan / Edition | Pricing Model | Deployment Target | Key Features Included |
|---|
| Community & Open Source | Free / Self-Hosted | Developers and early builders | Open-source code access, core compliance scripts, basic framework mapping |
| Cloud Startup | Tiered Subscription | Seed to Series A startups | 580+ automated integrations, AI policy generator, SOC 2 / HIPAA readiness, auditor room |
| Enterprise & Full Audit | Custom Annual | Scale-ups and enterprise teams | Included penetration tests, dedicated compliance manager, multi-framework coverage, SLA support |
Free diagnostic security tools and framework readiness calculators are accessible directly through the web application to evaluate initial audit timelines before full deployment.